Highlighted text? Practice this concept. Highlighted passages and figures open related questions.
Practice related questions (11)Progress & bookmarks
Current section
2 Information Security Measures
p. 383
Practice this section 11 linked exam questions with default filters
Progress
Not marked complete
Related questions in this lesson 1
CISO information-security responsibility1p. 383
2 Information Security Measures
Information security measures must be implemented comprehensively, so as to include not only information systems but also the environments surrounding people. An ISMS addresses three aspects: human security, technical security, and physical security from the perspective of information security measures.
2 - 1 Human Security Measures
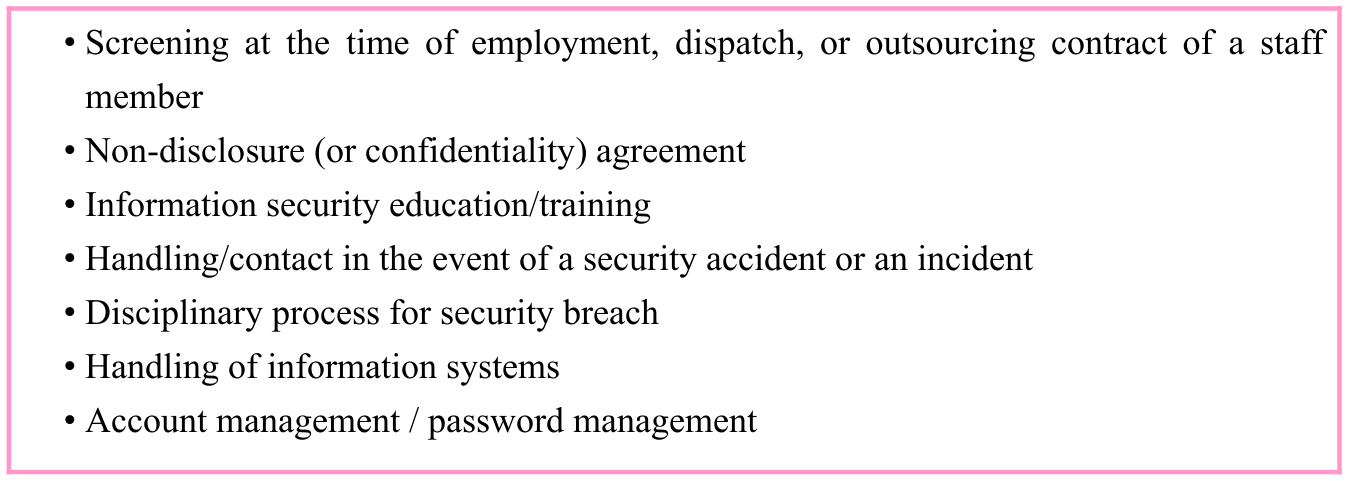
In the PDCA cycle of human security, information security policy is established at the ISMS planning (Plan) stage, and security education and training are implemented at the execution (Do) stage. Furthermore, the security compliance status of personnel is checked through log management and monitoring at the inspection (Check) stage. Any deficiencies or improprieties are handled and corrected at the Act stage. In human security measures, the greatest importance should be placed on information leakage by concerned parties. Information leakage due to inattention of concerned parties is difficult to completely prevent through agreements, rules, or information security education. As a measure against information leakage, unnecessary information disclosure should be avoided
p. 384
under the “need-to-know” principle. For example, appropriate access permissions should be set or important documents should be kept in a locked location. Such activities regarding information leakage measures are also important in acquiring the Privacy Mark (P Mark). The Privacy Mark system confers the mark on private or other businesses that have prepared an appropriate protection system for the handling of personal information.
Section progress
Original chapter exercises
Original chapter exercises →New FE Textbook Vol.1 · IT Fundamentals · First Edition, April 2015