Contents
Chapter 6 · SecurityPractice

LEARN WITH HARU

Video Lesson တွေက Haru အတန်းသားတွေအတွက်ပါ

Haru ရဲ့ ITPEC FE Full Course မှာ ယခု သင်ခန်းစာတွေကို တစ်ခုချင်း တစ်ကြောင်းချင်း အသေးစိတ်ရှင််ရှင်းပြထားပါတယ်

အခြေခံ မရှိတဲ့ ကျောင်းသားများစွာဟာလည်း ဒီ Course နဲ့ ပဲ အောင်မြင်ကုန်ကြပါပြီ

အတန်းမအပ်သေးပဲ Haru ဆီမှာ အစမ်းသင်ကြည့်ချင်ပါသလား?

သင်တန်းသားတွေရဲ့ စကားသံများ

သင်တန်းသားတွေရဲ့ စကားသံများ
Learning toolsProgress & bookmarks

Current section

1-4-2 Information Security Evaluation Criteria
p. 382

Progress

Not marked complete

Progress and bookmarks

p. 382

1-4-2 Information Security Evaluation Criteria

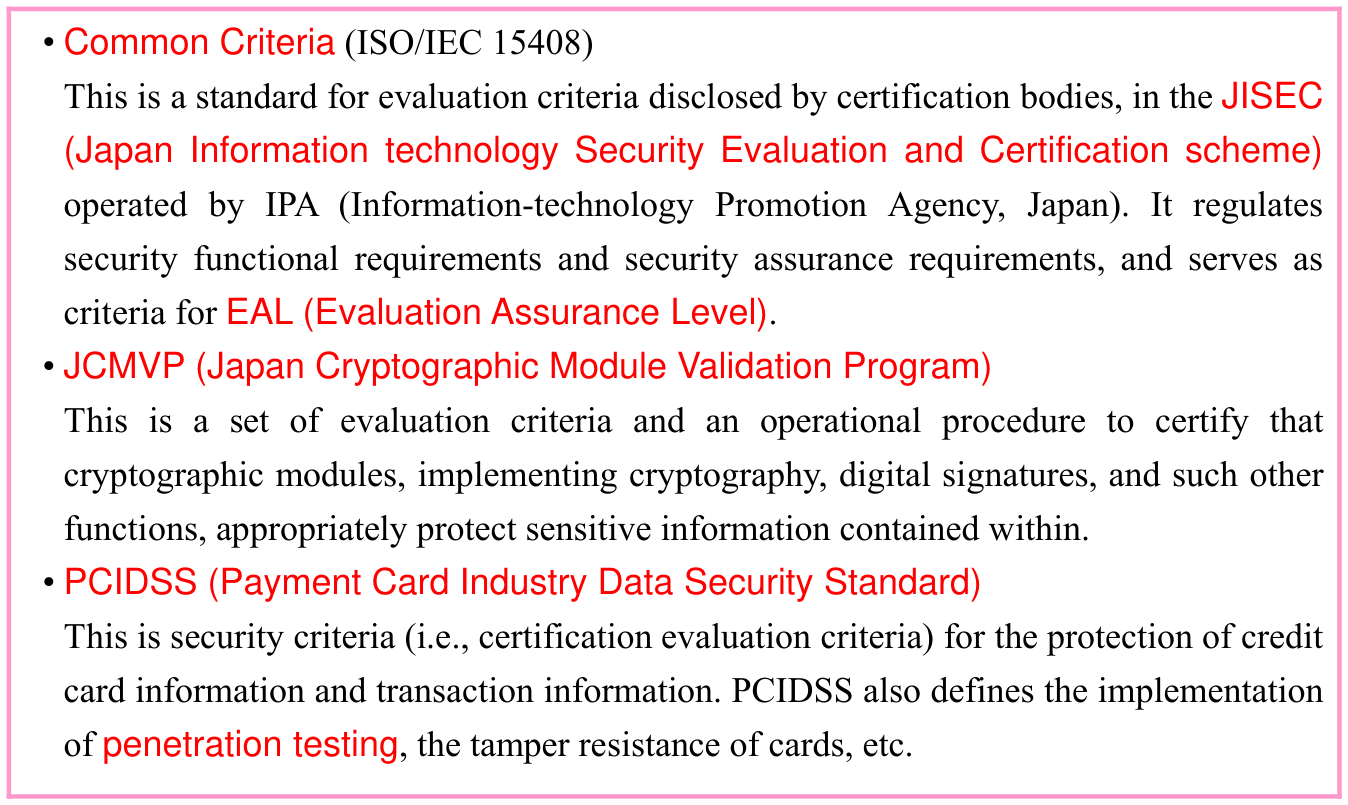
Original Security textbook callout or table, preserving the original labels, values, symbols and spatial arrangement. Source text: • Common Criteria (ISO/IEC 15408) This is a standard for evaluation criteria disclosed by certification bodies, in the JISEC (Japan Information technology Security Evaluation and Certification scheme) operated by IPA (Information-technology Promotion Agency, Japan). It regulates security functional requirements and security assurance requirements, and serves as criteria for EAL (Evaluation Assurance Level). • JCMVP (Japan Cryptographic Module Validation Program) This is a set of evaluation criteria and an operational procedure to certify that cryptographic modules, implementing cryptography, digital signatures, and such other functions, appropriately protect sensitive information contained within. • PCIDSS (Payment Card Industry Data Security Standard) This is security criteria (i.e., certification evaluation criteria) for the protection of credit card information and transaction information. PCIDSS also defines the implementation of penetration testing, the tamper resistance of cards, etc.
p. 382 · Enlarge

Section progress

Original chapter exercises

Original chapter exercises →

New FE Textbook Vol.1 · IT Fundamentals · First Edition, April 2015