Highlighted text? Practice this concept. Highlighted passages and figures open related questions.
Practice related questions (4)Progress & bookmarks
Current section
2-2 Service Management Processes
p. 352
Practice this section 4 linked exam questions with default filters
Progress
Not marked complete
Related questions in this lesson 4
Service continuity and availability management2Agreed service targets and improvement2p. 352 · PDF 358
2 - 2 Service Management Processes
In ISO/IEC 20000 (JIS Q 20000), service management processes are classified into four processes.
[Classification of service management processes]
1) Service delivery processes
2) Relationship processes
3) Resolution processes
4) Control processes
2-2-1 Service Delivery Processes
Service delivery processes are a group of processes for the service provider to deliver services that fulfill the customer requirements in a safe and continuous manner.
[Group of processes of service delivery processes]
1) Service level management
2) Service reporting
3) Service continuity and availability management
4) Budgeting and accounting for services
5) Capacity management
p. 353 · PDF 359
6) Information security management
(1) SLM (Service level management)
(2) Service reporting
In service reporting, the service provider produces a service report by using the information from the delivery of services and the service management processes, and then agrees with the interested parties about the report description. The service provider makes decisions and takes actions to improve services and deal with the problems on the basis of the findings in the service report.
[Description of service report]
- • Performance against service targets
- • Relevant information about significant events including major incidents (i.e.,
events that inhibit the service) and deployment of new or changed services - • Workload characteristics including volumes and periodic changes in workload
- • Detected nonconformities against the service requirements and their identified
causes - • Trend information
- • Customer satisfaction measurements, service complaints, and results of the analysis
of satisfaction measurements and complaints.
p. 354 · PDF 360
(3) Service continuity and availability management
- • BCP (Business Continuity Plan)
For continuing important business operations in the event of a disaster, a policy and an action plan are prepared so that disaster can be avoided beforehand or operations can be quickly recovered from the damage. System recovery methods include cold standby, which puts the system on standby without operating the spare system, warm standby, which puts the system on standby with the state of only starting the OS, and hot standby, which puts the system on standby in the same state as the production system. The recovery method is selected on the basis of the business operations to be
continued and the cost.
- • Business impact analysis (reduction of the impact of disaster)
In this analysis, the disaster scenario is anticipated, the permissible service stoppage time is decided, and the following countermeasures are prepared: constructing a backup center and preparing service recovery procedures.
On the other hand, in service availability management, the service provider prepares availability requirements and targets as an availability plan and monitors and evaluates availability, which is the indicator of availability, MTBF (Mean Time Between Failure), which is the indicator of reliability, and MTTR (Mean Time To Repair), which is the indicator of maintainability.
(4) Budgeting and accounting for services
In budgeting and accounting for services, the following services are implemented: a
budgeting service that plans and manages the budget for service delivery cost; and an accounting service for handling accounting processes. In this manner, financial management
p. 355 · PDF 361
(i.e., managing the financial condition) is efficiently conducted. In these services, costs are budgeted to enable effective financial management and decision-making for services to be delivered. In addition, a decision is made and the document is created concerning the apportionment of indirect costs and the allocation of direct costs to services for providing the overall cost of the service. This corresponds to “IT service financial management” in ITIL.
(5) Capacity management
In capacity management, the service provider identifies capacity and performance requirements, and maintains and manages the required capacity for fulfilling the requirements. The service provider prepares, implements, and maintains a capacity plan taking into consideration human, technical, information, and financial resources.
[Contents of capacity plan]
- • Current and forecast demand for services
- • Expected impact of agreed requirements for availability, service continuity, and
service levels - • Time-scales, thresholds, and costs for upgrades to service capacity
- • Potential impact of statutory, regulatory, contractual, or organizational changes
- • Potential impact of new technologies and new techniques
- • Procedures to enable predictive analysis, etc.
The service provider monitors the usage status of capacity, analyzes data, and performs tuning to provide sufficient capacity to fulfill requirements agreed on with the customer. In this case, the following are used as the capacity management indexes, such as CPU utilization, memory utilization, file utilization, network utilization. This data is centrally managed in CMDB (Capacity Management Database). Capacity management includes the following three subprocesses.
- • BCM (Business Capacity Management)
It is a subprocess that corresponds to capacity requirements of future business deployments. - • SCM (Service Capacity Management)
It is a subprocess that monitors and evaluates the usage status of an IT service in order to fulfill the capacity requirements stated in SLA. - • CCM (Component Capacity Management)
It is a subprocess that monitors and evaluates the usage status of IT resources (i.e.,
p. 356 · PDF 362
components), such as hardware, and handles the problems related to IT resources.
(6) Information security management
In information security management, the service provider implements and operates the information security controls for preserving confidentiality, integrity, and availability (or accessibility) of information assets.
| Confidentiality | The property of making information unusable by, or undisclosed to, unauthorized parties |
|---|---|
| Integrity | The property of protecting the accuracy and completeness of assets |
| Availability | The property of enabling access and use when requested |
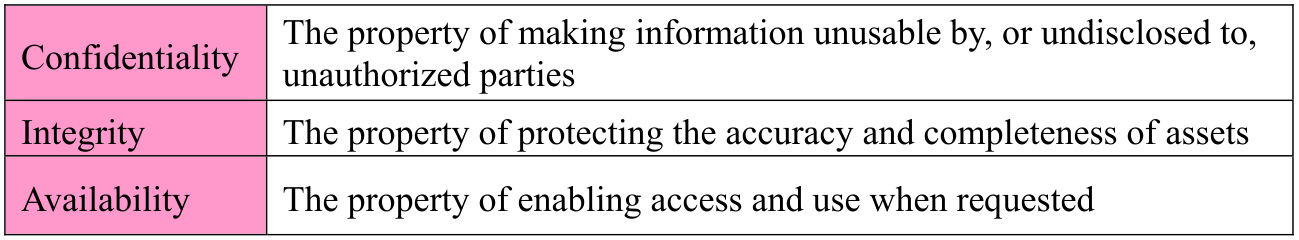
Management with appropriate authority approves an information security policy (i.e., document that identifies information assets to be protected by the organization, reasons to be protected, and approaches to information security) by taking into consideration the service requirements, statutory and regulatory requirements, and contractual obligations. Furthermore, management communicates the approved information security policy to the service provider, the customer, and the internal staff members and ensures that everyone complies with it. On the other hand, while fulfilling the requirements of the information security policy, the service provider implements and operates physical, administrative, and technical information security controls in order to preserve confidentiality, integrity, and availability (or accessibility) of information assets.
[Example of information security controls]
- • Physical entrance and exit control
- • Network security solution
Service and business operator that offers the mechanism of network security (e.g., tapping measures, spoofing measures, falsification measures) - • User access management
- • User authentication
- • User password management
- • Privilege management
Technique of managing “privilege,” the most powerful authority related to information system in order to protect unauthorized use by a third party - • Access control
- • Protection of log information
- • Measures against malware
p. 357 · PDF 363
With regard to requests for change of the information security, the following are evaluated and identified: new or changed information security risks, and potential impact on the existing information security policy and controls. Information security incidents (i.e., events that inhibit the service and are attributable to information security) are managed according to the incident management procedures and priority appropriate to the information security risks. In this case, the service provider analyzes the type, frequency of occurrence, and impact of an information security incident, and then reviews it after reporting and recording in order to identify opportunities for improvement.
Section progress
Original chapter exercises
Original chapter exercises →New FE Textbook Vol.2 · First Edition, April 2015